Skip to content
Sign in

Human-led, AI-enhanced security

Know where you stand on cyber security, and what to do next.

Assessments, identity monitoring, policies and a clear security score in one secure place. AI does the heavy lifting; our specialists make the calls.

Invited to GoRaC? Sign in with your work email address.

Mapped to the standards UK organisations are measured against, and the services they run on

  • Cyber Essentials
  • ISO 27001
  • NCSC guidance
  • Microsoft 365
  • Entra ID
  • Google Workspace
  • Okta

Enhanced by AI, led by people

AI reads the detail at a speed no team can match. Our specialists check it, decide what matters for you and stay accountable for it.

  1. AI does the reading

    It works through every answer, setting and sign-in alongside current threat intelligence, and drafts your report and policies, in minutes rather than days.

  2. Specialists make the calls

    A named specialist checks the analysis, decides what matters for your organisation and signs off everything before you see it.

  3. Nothing changes without a person

    AI never touches your systems. Any fix we make is asked for with a reason, approved by our senior team and recorded.

  4. Your data, protected

    AI only sees what a task needs, your evidence files are never sent to it, and what you write is treated as information, never as instructions.

Everything you need, in one place

From your first assessment to a score that keeps itself up to date.

Assessments

Cyber Essentials readiness and wider cyber threat reviews, answered in a secure portal or completed with one of our specialists.

  • Plain-English questions, saved as you go
  • Colleagues answer side by side
  • Attach supporting files to any answer

Identity and Microsoft 365 monitoring

Read-only connections to Microsoft 365, Google Workspace and Okta that check the people, apps and settings behind most real-world attacks, every day.

  • How strongly everyone signs in, and who holds admin rights
  • Gaps and changes in your sign-in policies, flagged the same day
  • Apps and service accounts that sign in without a person
  • Tenant settings checked against recognised benchmarks
  • Devices, compliance and antivirus where Intune is licensed

Early warning of account takeover

The tell-tale signs of a hijacked mailbox or leaked password, spotted early and passed to a specialist straight away.

  • Hidden inbox rules and mail forwarded outside
  • Unusual sign-ins, such as from a new country
  • Addresses at your domains found in known data breaches

Joiners, leavers and access reviews

Every few months you confirm who should keep access: admins, guests and connected apps. Choose Keep, Remove or Not sure, and we follow up the rest.

  • Leavers' accounts checked until they're switched off
  • New starters set up with multi-factor sign-in
  • A record of every review for your auditor or insurer

Fixes, not just findings

When something needs changing in Microsoft 365, we can do it for you, with access your admin grants separately and can remove at any time.

  • Block a leaver's sign-in or sign someone out everywhere
  • Remove a suspicious inbox rule, guest or app
  • Every change approved by a person and recorded

A security score

One number out of 100, fair to your size and licences, with a ranked list of what would make the biggest difference next.

  • Based on outcomes, not products
  • The fundamentals come first
  • Every point explained

Policies that fit

Security policies tailored to how you actually work, reviewed and accepted in the portal, with reminders when they're due for review.

  • Shorter versions for small businesses
  • Ask staff to read and confirm them
  • Already have your own? Upload them

Clear reports

Drafted with AI and current threat intelligence, then reviewed and signed off by a specialist: plain-English findings and a prioritised plan you can share with your board or insurer.

  • Cyber Essentials readiness
  • What to fix first, and why
  • Security features you may already be paying for

Turn findings into progress

Assess once, keep watch every day, and improve with a plan that's ranked for you.

Assess

Answer once, together

In the portal at your own pace, or completed with one of our specialists.
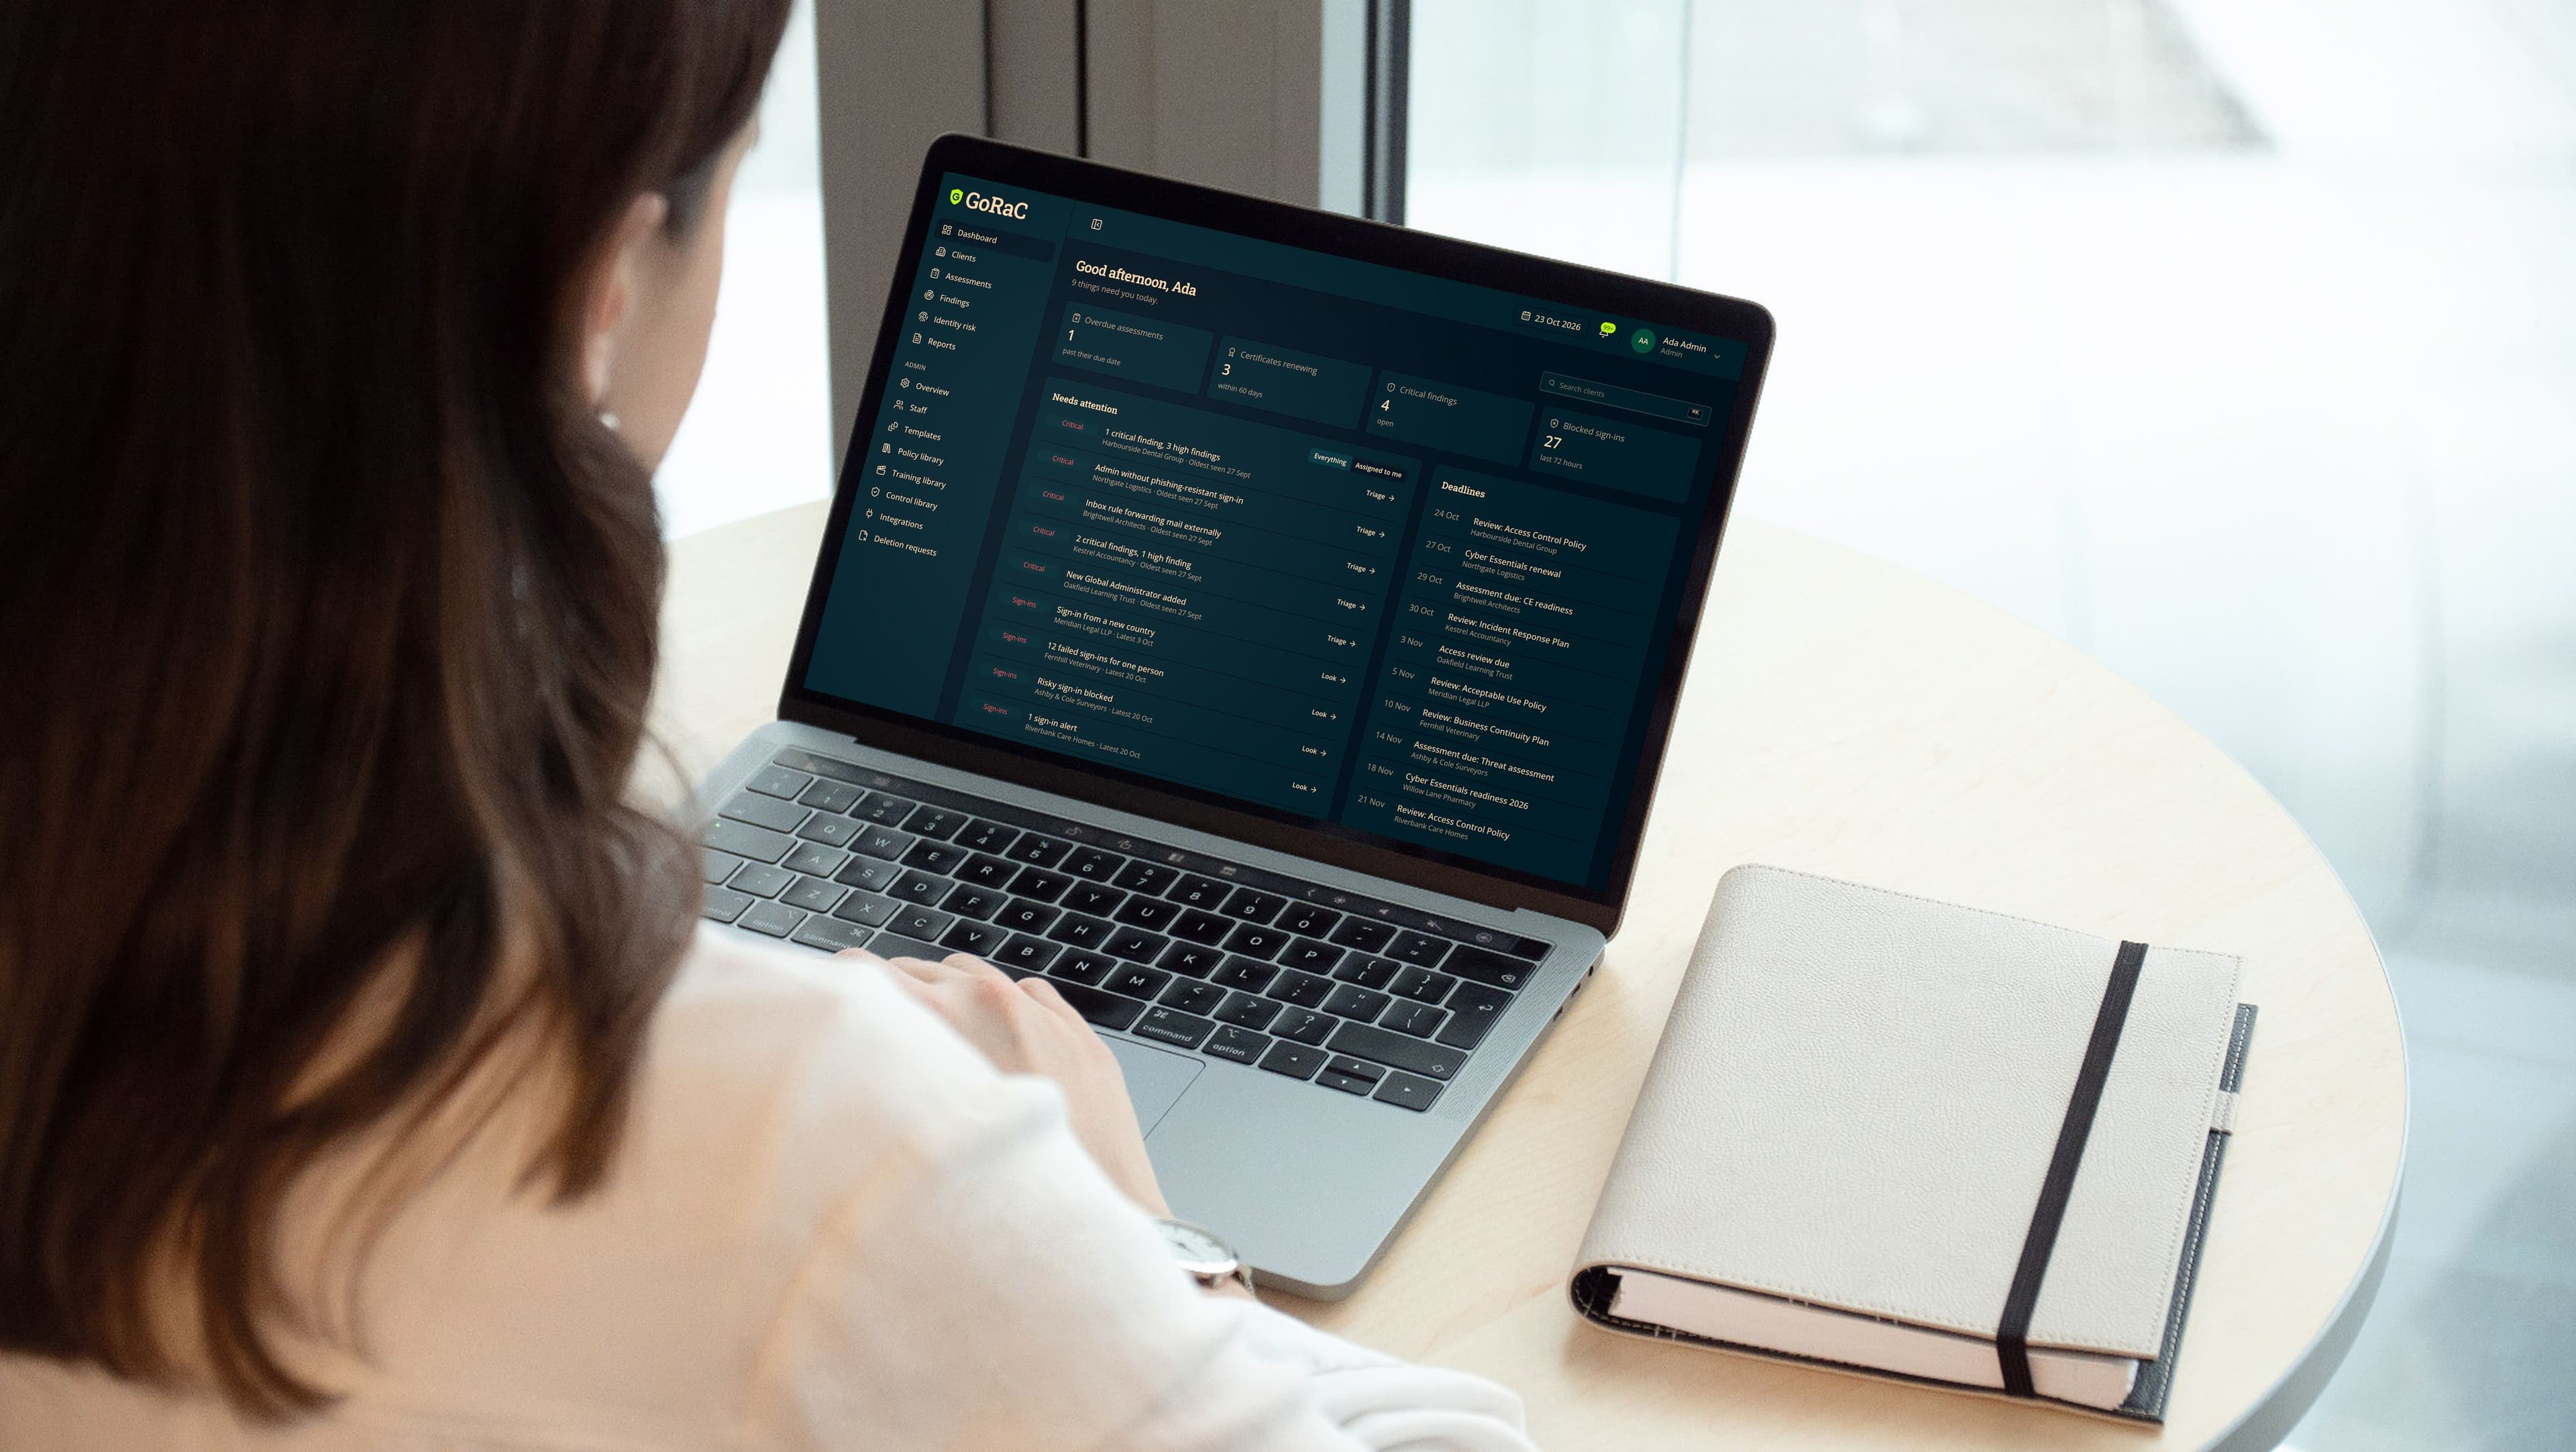
Monitor

Checked every day

Read-only connections to Microsoft 365, Google Workspace or Okta spot risky changes before they become a problem.

Improve

A plan ranked for you

Every point explained, with the actions worth the most listed first.

See every area at a glance

Your security score is built from ten areas, so you can see where you're strong and where the gaps are.

  • Weighted so the basics that stop most attacks, like sign-in security and updates, count most.
  • Updated as monitoring runs, so the picture moves when you fix something.
  • Every gap comes with its next step and the points it's worth.
  • Shared in your portal once we've reviewed it.
Score by areaFirst assessmentThree months on
Example score by area: every area improves between the first assessment and three months on.Identity and access: 45 at the first assessment, 86 three months onIdentityDevices and secure set-up: 55 at the first assessment, 78 three months onDevicesUpdates and supported software: 60 at the first assessment, 84 three months onUpdatesMalware protection: 80 at the first assessment, 92 three months onMalwareNetwork and firewalls: 70 at the first assessment, 80 three months onNetworkEmail and data protection: 40 at the first assessment, 76 three months onEmail and dataBackup and recovery: 50 at the first assessment, 72 three months onBackupPolicies: 30 at the first assessment, 74 three months onPoliciesPeople and awareness: 35 at the first assessment, 68 three months onAwarenessMonitoring and response: 40 at the first assessment, 75 three months onMonitoring

Scores out of 100. An illustrative example, not a real organisation.

Example score by area, out of 100
AreaFirst assessmentThree months on
Identity and access4586
Devices and secure set-up5578
Updates and supported software6084
Malware protection8092
Network and firewalls7080
Email and data protection4076
Backup and recovery5072
Policies3074
People and awareness3568
Monitoring and response4075

Fits the way you already work

No new passwords, no software to install, nothing to change in how you run Microsoft 365, Google Workspace or Okta.

  • Microsoft 365, Google or Okta

    Your admin approves read-only access once, and can remove it at any time.

  • Sign in with a code

    A one-time code to your work email. Nothing to remember, nothing to reset.

  • Answer together

    Invite colleagues and see each other's answers as they happen.

  • Policies as PDFs

    Read, accept or ask for changes in the portal, and keep a PDF for your records.

  • Access reviews in minutes

    Confirm who should keep access with one choice per person or app. We follow up the rest.

  • Analysis you can question

    AI speeds up the reading; a specialist you can talk to explains every finding and decision.

Ready to see where you stand?

Invited by GoRaC? Enter your work email to sign in.

Built for trust, by design

Security isn't a feature we added. It's how the platform is built.

  • Data residency respected

    Your data is hosted with your organisation's data residency requirements in mind.

  • Kept apart

    Each organisation's information is isolated at the database level, not just hidden on screen.

  • Read-only by default

    Monitoring can read settings but never change them. Write access for fixes is separate, optional and yours to remove.

  • Private file storage

    Uploaded files are never public, and download links expire within minutes.

  • AI with guard rails

    AI never acts on its own and never sees your evidence files. A specialist reviews what it produces before you do.

  • Every change accountable

    Every fix is asked for with a reason, approved by our senior team and kept in an audit trail you can ask to see.

Read our privacy notice for how we use personal information.

How it works

Four steps, with AI doing the legwork and a specialist alongside you the whole way.

  1. Connect and set up

    We set up your assessment and, if you use Microsoft 365, Google Workspace or Okta, your admin approves a read-only connection once.

  2. Answer, or we do it together

    Your team answers in the portal at their own pace, or we sit down with you and complete it on your behalf.

  3. AI analyses, we decide

    AI cross-checks every answer with what monitoring shows and current threats. Our specialists review it, decide what matters and work out your score.

  4. Act, then keep improving

    You get a report, the policies you need and a clear to-do list. Monitoring, access reviews and our team keep it current.

More than a one-off audit

An audit tells you where you stood on the day. GoRaC keeps telling you.

What GoRaC adds to a one-off audit
FeatureOne-off audit
A detailed assessment by a specialistYesYes
Sign-in, admin and app access checked every dayNoYes
Hijacked mailboxes and leaked passwords spotted earlyNoYes
AI-assisted analysis, checked by a specialistNoYes
A score that updates as things changeNoYes
Policies tailored, accepted and reviewed on timeNoYes
A to-do list ranked by what matters mostYesYes
Staff asked to read and confirm policiesNoYes

Frequently asked questions

How do you use AI?
To read and cross-check the detail: your answers, settings, sign-ins and current threat intelligence, and to draft reports and policies. A specialist reviews everything before you see it, AI never changes anything in your systems, and your evidence files are never sent to it.
What does GoRaC need from Microsoft 365?
Your administrator approves read-only access once. We can read the settings that matter, but never change anything, and your admin can remove the connection at any time.
We use Google Workspace or Okta. Does that work?
Yes. Both connect read-only, alongside or instead of Microsoft 365, and your admin can remove the access at any time.
Do you check apps as well as people?
Yes. We list every app that can reach your data on its own, check how it signs in, who owns it and whether it's still used, so forgotten access doesn't linger.
Would you notice if someone took over a mailbox?
We look for the signs: inbox rules that hide mail or forward it outside, especially straight after a sign-in from somewhere new. When we see them, a specialist is alerted straight away.
What happens when someone leaves?
Tell us, or we'll spot it in your access review. Until their account is switched off it stays on your to-do list, and if you've given us write access, we can switch it off for you.
Where is our data kept?
With established cloud providers, hosted to respect your organisation's data residency requirements. Each organisation's information is kept apart from every other's at the database level.
How do we sign in?
With a one-time code sent to your work email. There's no password to remember or reset.
We're a small business. Is the score fair to us?
Yes. It's measured against what's reasonable for an organisation of your size and licences, so a well-run small business can score as highly as a large one.
We already have our own policies. Can we use them?
Yes. Upload them in the portal and, once we've reviewed them, they count towards your score.
Can we download our policies?
Yes, as a PDF with the document control details and change history, whenever you need them.

Security analysis enhanced by AI, led by people

Sign in